A worked example: where the task becomes difficult
A fictional API change adds export filtering. The pull request includes a passing test but also broadens which records are returned to an authenticated user. The reviewer needs to inspect authorization, output format and pagination, not just confirm the new date parameter exists. Compare the patch with the approved request and check whether unrelated environment or dependency changes have been included.
Decisions to make before implementation
Separate implementation review, test evidence and release readiness. The author should explain what changed and why; the reviewer should independently check high-impact boundaries. Inspect removed lines as carefully as additions, especially deleted access checks or validation. Decide which evidence must be produced on a deployed environment and which can be established with controlled tests before merge.
A practical sequence for the work
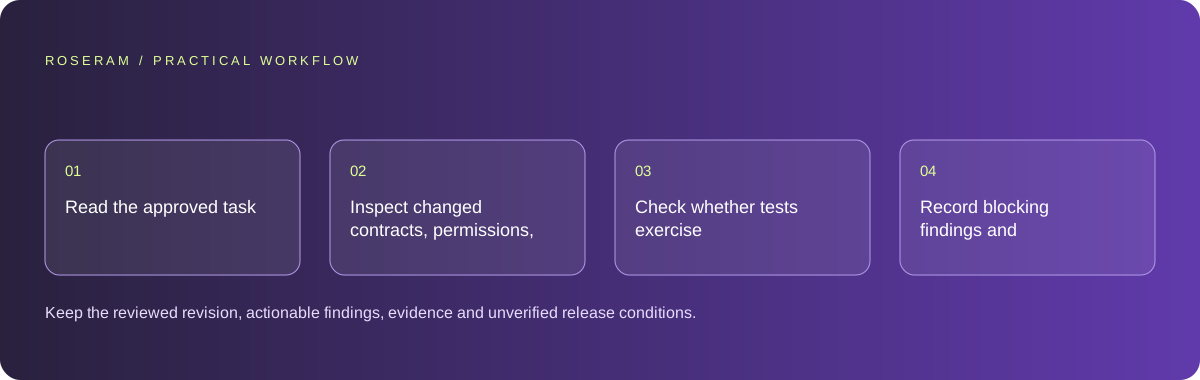
Use the sequence below as a task boundary, not as a claim that the example has been executed. Work with approved inputs and the project’s actual architecture. If a required integration or permission is unavailable, keep that stage visibly incomplete rather than generating a plausible substitute result.
- Read the approved task and summarize the intended behavior independently.
- Inspect changed contracts, permissions, dependencies and external side effects.
- Check whether tests exercise failure paths and the original reported problem.
- Record blocking findings and release checks before approving the revision.
A detailed brief you can adapt for your agent
Replace the illustrative context with your approved facts and controlled inputs. Keep the stated boundaries when adapting the brief. The expected deliverable matters more than a particular tool name: ask for an explanation grounded in the inspected material and evidence for the requested outcome.
Review this export-filter pull request against the supplied acceptance criteria. Inspect authorization, pagination, output compatibility and deleted safeguards. Evaluate the tests without assuming their assertions are correct. Return file-specific findings with evidence and severity. Do not modify or merge the pull request during the review.Failure modes that an attractive preview can hide
An AI-generated test can mirror the implementation so closely that both share the same mistaken assumption. Use a requirement-derived example with independently calculated expectations. Beware of large “cleanup” patches that obscure removed safeguards. A review performed before the last commit is not evidence for a materially changed final revision; tie approval and results to the reviewed commit.
Technical references: GitHub: pull request reviews
Acceptance checks and the evidence to retain
Keep the reviewed revision, actionable findings, evidence and unverified release conditions. An approval should identify the scope actually reviewed, not imply a complete security audit.
| Controlled case | Expected evidence |
|---|---|
| Export is requested by a limited account | Only permitted records appear in the result. |
| Date filter excludes every record | Output remains valid and accurately empty. |
| New commit changes authorization after review | The approval workflow requires review of the changed revision. |
Specific answers
Common questions
Do passing tests make a pull request safe?
They establish only the behavior those tests meaningfully cover; inspect the product and access contracts too.
Can the same agent review its own changes?
It can help, but independent checks of critical assumptions add useful evidence.
What is the practical completion criterion?
Keep the reviewed revision, actionable findings, evidence and unverified release conditions. An approval should identify the scope actually reviewed, not imply a complete security audit.
Sources and editorial method
These references support the indicated technical facts. Workflows, examples and decision tables are original Roseram analysis. Illustrative costs are not vendor prices. No search volume, organic difficulty, ranking result or product endorsement is implied.
- GitHub: pull request reviews ↗
Review and approval concepts; passing checks are not a universal security certification.
Roseram offers AI software and may compete with tools discussed here. Sources checked 2026-10-11. Send a sourced correction.
Your next step
Keep a practical checklist.
Mark your progress. This checklist and helpfulness choice are saved on this device only; they are not public reviews.
0 of 5 complete
Share your experience in the community or submit a sourced correction. Public experiences remain separate from editorial claims.
Bring your next idea
Keep learning. Build with context.
Get Roseram model and workspace reopening updates. The guide remains available whether or not you subscribe.
Explore the workspace guide →